
Optimizely Incident Response: What Evidence Closes Your Website Incident?
By CellWall Security Research | Published November 19, 2026 | Client-Side Security | 5 min read
A vendor’s remediation statement is one input to your incident record. To close your own investigation, document which projects and pages used the affected service, what evidence exists for the relevant period, which response actions you verified, and which questions remain unanswered. A clean page today does not reconstruct an earlier visit.
Start with a dated, attributed account
In its November 18 update, Optimizely attributed the November 16 incident to abuse of its Web Experimentation signup flow that enabled impersonation and malicious project JavaScript. The vendor reported remediation and distinguished the event from a credentials breach. These are Optimizely’s statements about its service, rather than a finding about each customer’s visitors. Vendor incident record.
Report URI’s original investigation describes saved script samples and several loader variants. StepSecurity’s analysis separates captured payloads from requests without a retained response. Their findings make evidence coverage important: an observed request and a recovered script answer different questions. Report URI investigation, StepSecurity analysis.
Use the following worksheet as an investigation structure, not a statement that your organization was affected or that any particular visitor lost data.
Build one record for each project and journey
Assign an incident owner and an evidence custodian. Keep sensitive captures in approved incident storage, with a redacted summary in the working record. For each entry, include an observation time and time zone, source, collector, and limitation.
Was this project in scope?
Evidence to seek: Project identifier, vendor notification and deployment/configuration history. Without it: Whether use of the vendor involved the affected project.
Which pages used it?
Evidence to seek: Inventory, application configuration and historical page/script observations. Without it: Which user journeys might have received it.
What content was delivered?
Evidence to seek: Preserved script responses, timestamps, headers and comparable digests. Without it: What the same URL served earlier or to another session.
What ran or communicated?
Evidence to seek: Existing browser observations and retained request records, with test conditions. Without it: Whether a request executed a payload or transferred sensitive data.
What changed during response?
Evidence to seek: Approved control changes, deployment records and repeat observations. Without it: Whether a proposed containment action actually took effect.
Who accepts the residual gap?
Evidence to seek: Named decision owner, rationale and next review date. Without it: Whether unresolved uncertainty has been deliberately accepted.
A missing historical capture should remain a missing capture. Do not replace it with a current download and label it historical. Likewise, identify whether a timestamp describes collection, publication, detection or an asserted event. Keep conflicting observations alongside their sources until they can be reconciled.
Separate containment, exposure and impact
Use three sections in the case record:
Containment
Record the action, its owner, when it was applied and what subsequent evidence supports its effect. Distinguish the vendor’s change from a change your team made.
Potential exposure
List the relevant projects, pages, periods and conditions supported by evidence. Mark inferred boundaries as estimates and explain their basis.
Observed impact
Record findings supported by your investigation. Payload capability alone does not establish that a specific user lost data. A lack of retained telemetry also does not establish that no loss occurred.
Review each statement with the team responsible for it. Security can describe technical observations; privacy, legal and payment stakeholders may have separate decisions to make. This worksheet makes no compliance determination or notification decision.
Test a recovery claim within a defined scope
On systems you are authorized to test, agree a small set of representative journeys and approved test data. Record browser/version, account state, relevant consent state, application release and the furthest step reached. Preserve the baseline before changing controls, then repeat the same journeys after the change.
Explain the result in terms of those conditions: what loaded, what changed and which destinations were observed. Keep untested journeys visible. A present-day test can support a recovery observation within its scope; it cannot prove the contents of every previous visitor session.
Close with an evidence decision
Before closing the technical investigation, ask whether the record has a named owner, supported scope, documented response actions, a retained evidence index and an explicit list of gaps. Assign any follow-up a person and a review date. If historical exposure remains unresolved, state that directly rather than treating vendor cleanup as its substitute.
For ongoing monitoring design, see JavaScript change detection. For interpreting test coverage, see what a clean checkout scan can miss. These guides complement the incident worksheet; they do not establish the outcome of this incident for your organization.
Does a trusted script domain prove the script was safe?
No. Identify the version delivered and the conditions of observation. A familiar source name is not a historical content record.
Can a clean test close every exposure question?
No. Record the tested journeys and period, then separately evaluate the historical evidence and unresolved gaps.
Does this establish a PCI DSS violation?
No. Technical observations need to be evaluated against the organization’s actual scope and applicable obligations. This article makes no compliance finding.
Continue exploring
Read the practical guides that clarify the surrounding risks, controls, and evidence.
Explore the client-side security hub
Client-Side Security
JavaScript Change Detection: Hash Monitoring vs. Behavioral Monitoring
Compare JavaScript hash monitoring with behavioral monitoring, understand what each method detects and misses, and build a practical hybrid workflow for first- and third-party scripts.
Client-Side Security
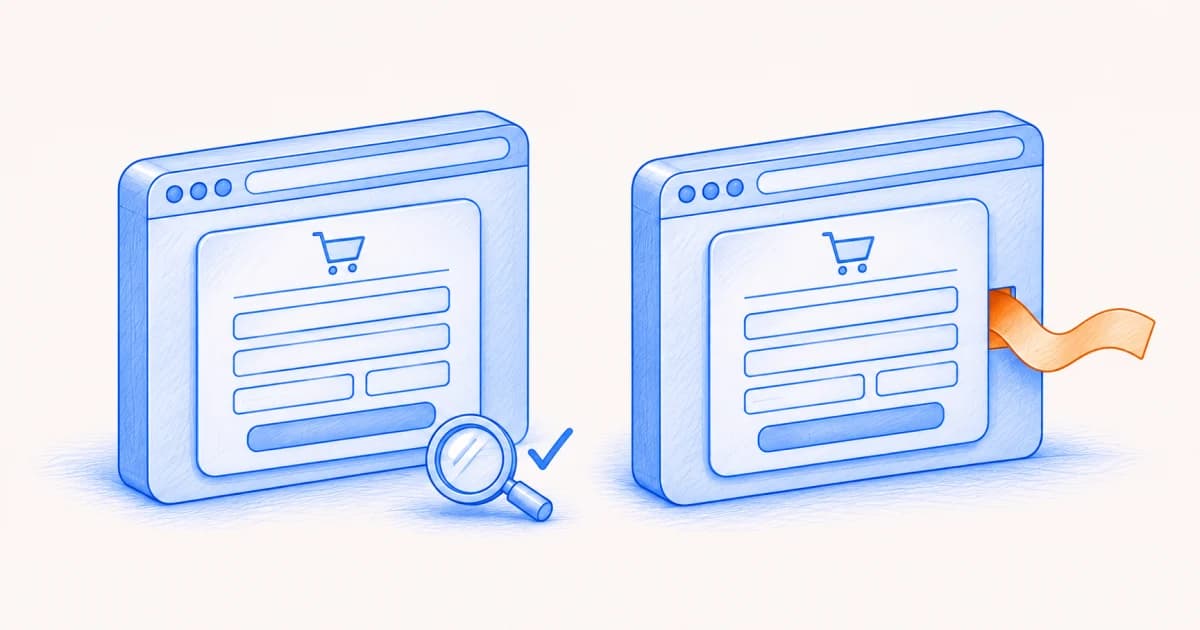
What a Clean Checkout Scan Can Miss
A Magento loader could respond differently to automated browsers. Learn how to compare sessions and describe what a clean synthetic checkout monitoring result actually covers.
Client-Side Security
SuperPixel: When Your Own jQuery Becomes a Card Skimmer
SuperPixel changed JavaScript at an approved URL and replaced the checkout form. Learn how payment page tamper detection can connect changed script bytes, a new form, and unexpected requests.