
Google Consent Mode v2: Demystifying Basic vs. Advanced Implementation
By CellWall Team | Published June 25, 2026 | Compliance | 5 min read
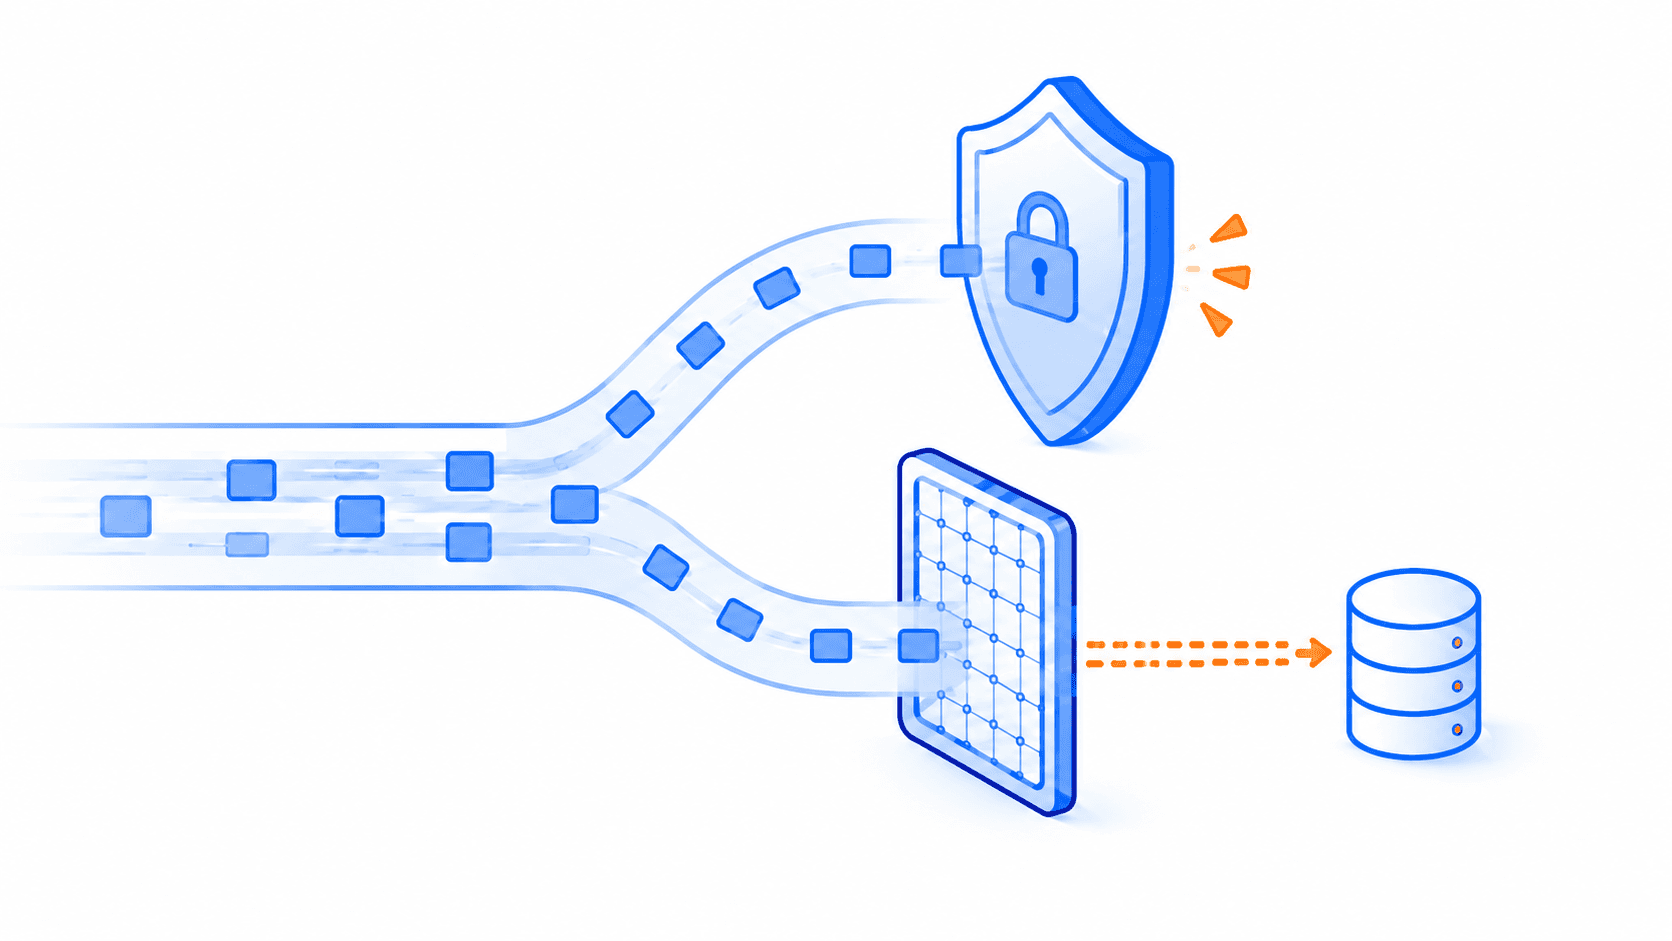
With the enforcement of the European Union's Digital Markets Act (DMA), privacy has evolved from a passive legal requirement into an active technical gatekeeper. For organizations utilizing Google Analytics 4 (GA4) or Google Ads, the most immediate consequence of this shift is the mandate to support Google Consent Mode v2.
Without Consent Mode v2, websites cannot transmit the explicit consent signals (ad_user_data and ad_personalization) required to build audiences, retarget visitors, or maintain accurate attribution in European territories.
However, when preparing to implement this protocol, engineers and privacy officers are faced with a pivotal architectural decision: Should you deploy Basic Consent Mode or Advanced Consent Mode? This article provides an objective, educative breakdown of both modes, analyzing their technical mechanisms, conversion modeling benefits, and legal implications to help you choose the correct approach for your stack.
The Technical Core: What is Consent Mode v2?
At its foundation, Consent Mode v2 is an API that allows your website to communicate visitor cookie consent choices directly to Google’s tags. It introduces two new parameters alongside Google's legacy storage flags: ad_storage (advertising cookies), analytics_storage (analytics cookies), ad_user_data (user personal data sent to Google for ads), and ad_personalization (remarketing permission).
When a user interacts with a consent banner, the banner must fire a gtag('consent', 'update', ...) command containing these parameters to adjust the behavior of downstream Google scripts in real-time. After implementation, test whether the cookie banner actually blocks tracking rather than relying on its visible state.
Basic Consent Mode: Complete Script Gatekeeping
In Basic Consent Mode, Google scripts are prevented from loading or executing until the user explicitly interacts with your consent banner and clicks "Accept." If the visitor ignores the banner or clicks "Decline," zero network requests are sent to Google, and no telemetry is collected.
Basic Mode offers the lowest legal risk. Since no network requests or IP addresses are sent to Google before or after a rejection, there is zero risk of unconsented data transmission, satisfying even the most conservative data protection officers.
While safe, Basic Mode requires robust tag-blocking configurations. Developers must set up custom trigger logic inside GTM (or manually modify script wrappers) to prevent Google tags from firing prematurely. This creates additional maintenance overhead for product releases.
Advanced Consent Mode: The Signaling Bridge
In Advanced Consent Mode, Google tags are allowed to load immediately when the page loads, even before the visitor has interacted with the banner. If consent has not yet been granted, the tags adjust their behavior—they avoid reading or writing cookies and instead transmit anonymous, stateless "pings" to Google's servers to allow for conversion modeling.
Advanced Mode represents a complex regulatory grey area in Europe. Several European Data Protection Authorities (DPAs), including France's CNIL, have explicitly stated that transmitting network telemetry or modeling conversion data prior to user opt-in can violate GDPR consent standards. If your legal team is risk-averse, Advanced Mode may require formal executive approval.
Direct Comparison: At a Glance
| Feature | Basic Consent Mode | Advanced Consent Mode |
|---|---|---|
Tag Loading Behavior | Tags are blocked until opt-in is explicitly received. | Tags load immediately with default 'denied' state. |
Telemetry on Rejection | Zero network requests sent to Google. | Stateless metadata 'pings' sent without cookies. |
Data Loss Rate | 100% loss of declined traffic. | ~30% loss (70% recovered via Google's AI models). |
Legal/Regulatory Risk | Extremely low risk. | Moderate-to-high risk in strict EU jurisdictions. |
Implementation Complexity | High (Requires tag blocking logic in GTM/CMS). | Moderate (Requires precise loading sequencing). |
Implementation Best Practices: Avoiding the Race Condition
Regardless of which mode you choose, the most common engineering failure point in Consent Mode v2 is the Race Condition. If your Google Tag fires before your default denied script executes, Google's servers will receive a fully tracked, cookie-based ping before your compliance preferences are registered. In addition to following the correct sequence, teams can automate consent checks in Playwright to catch this failure in repeatable tests. To prevent the race condition, developers must strictly adhere to the following sequence:
Set Defaults Instantly
Inject the gtag default denied configuration at the absolute top of your HTML <head> before any GTM or Google scripts load.
Load GTM/Google Tags
Load your standard Google Tag Manager container. In Advanced Mode, GTM will fire tags in a restricted state, sending only stateless pings.
Render cookieWall Banner
cookieWall initializes, checks local storage for saved preferences, and displays the banner if no previous choices exist.
Update Consent State
Upon user action (Accept/Decline), cookieWall dynamically fires gtag('consent', 'update', ...) to grant or revoke script permissions.
<!-- 1. Place this at the very top of your HTML <head> -->
<script>
  window.dataLayer = window.dataLayer || [];
  function gtag(){dataLayer.push(arguments);}

  // Set default denied state
  gtag('consent', 'default', {
    'analytics_storage': 'denied',
    'ad_storage': 'denied',
    'ad_user_data': 'denied',
    'ad_personalization': 'denied',
    'functionality_storage': 'denied',
    'personalization_storage': 'denied',
    'security_storage': 'granted' // Necessary is always allowed
  });
</script>

<!-- 2. Load GTM safely under the default block -->
<script async src="https://www.googletagmanager.com/gtm.js?id=GTM-XXXXXX"></script>Ready to deploy client-side consent?
Deploy cookieWall in under 5 minutes. It handles Google Consent Mode v2, Meta Pixel, and Microsoft UET out-of-the-box, ensuring zero-overhead script blocking and full compliance. Start your free trial today.

Useful Documentation & Resources
Continue exploring
Read the practical guides that clarify the surrounding risks, controls, and evidence.
Compliance
Cookies Aren't the Whole Story: How Browser Tracking Works Without Them
Learn how browser storage, pixels, network identifiers, service workers, link decoration, and fingerprinting signals can support tracking beyond traditional cookies.
Compliance
Automated Cookie Consent Testing with Playwright: Catch Regressions Before Release
Build Playwright tests that verify consent choices across cookies, browser storage, scripts, and network requests in pull requests and scheduled production checks.
Compliance
Is Your Cookie Banner Actually Working? A Practical Consent Compliance Test
Use browser DevTools and a repeatable test matrix to verify that your consent banner blocks non-essential cookies, storage, scripts, and data transfers.